When does OSINT research help?
When digital exposure, sources and connections must be mapped and documented to understand how information is circulating.
Isolated data rarely tells the full story. Through OSINT research and source correlation, I examine information exposure and potential risks affecting people, businesses and organizations.
An OSINT specialist helps establish where information comes from, how it relates to other records and what its context may mean. Andrea Mavilla conducts digital research and correlates information while documenting the evidence and its relevance.
In Threat Intelligence, information becomes useful when assessed against exposure, threat scenarios and possible consequences for individuals and organizations. Finding exposed information does not, by itself, prove unauthorized access or a breach.
When digital exposure, sources and connections must be mapped and documented to understand how information is circulating.
Threat context, digital exposure, possible data misuse and risks including impersonation or targeted phishing.
A documented picture of relevant findings, source references, limitations and the risk context they may inform.
A telephone number listed by a third-party service or an exposed email address can create risks, but does not by itself prove an attack on an organization’s systems.
Identify public references to people, roles, organizations and technology. The aim is to understand where information appears and how it may be linked.
Compare public sources, dates, metadata and consistency. Distinguish an isolated signal from a pattern supported by evidence.
Examine possible consequences, including impersonation, identity exposure, targeted phishing and reputational harm. Conclusions remain proportional to the evidence.
Useful research keeps observations, hypotheses and confirmed findings separate.
Clarify research objectives, authorized sources, risk categories and limitations.
Document accessible sources, URLs, dates and the context needed for review.
Review connections and alternative explanations rather than confusing exposure with compromise.
Present a risk assessment distinguishing observations, possibilities and uncertainty.
Interface visuals and terminal commands are illustrative; they do not perform live scans. Research does not involve unauthorized access.
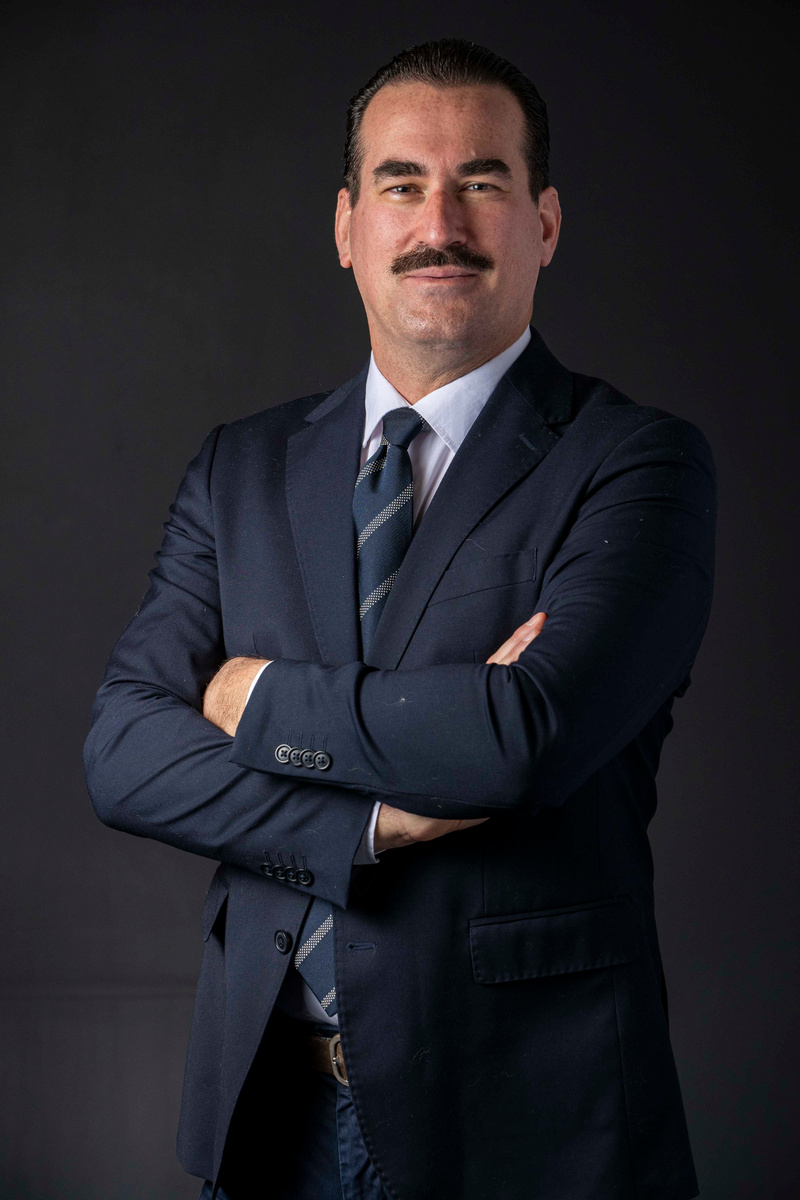 Andrea MavillaProfessional background and method ↗
OSINT describes research and analysis techniques using accessible sources. Cyber Threat Intelligence draws on multiple sources, including OSINT, to inform threat assessments and decisions.
No. Public accessibility alone does not demonstrate intrusion or a breach of an organization’s systems. Additional evidence would be needed to establish the cause.
Organizations, businesses, professionals and public-facing individuals seeking to understand what information is discoverable and what risks might arise from its correlation.
The approach described relies on lawful sources, documentary review and authorization where required. It does not involve unauthorized access to systems or accounts.
We can define the scope of a review, the open sources that may be relevant and the questions that require a documented answer.