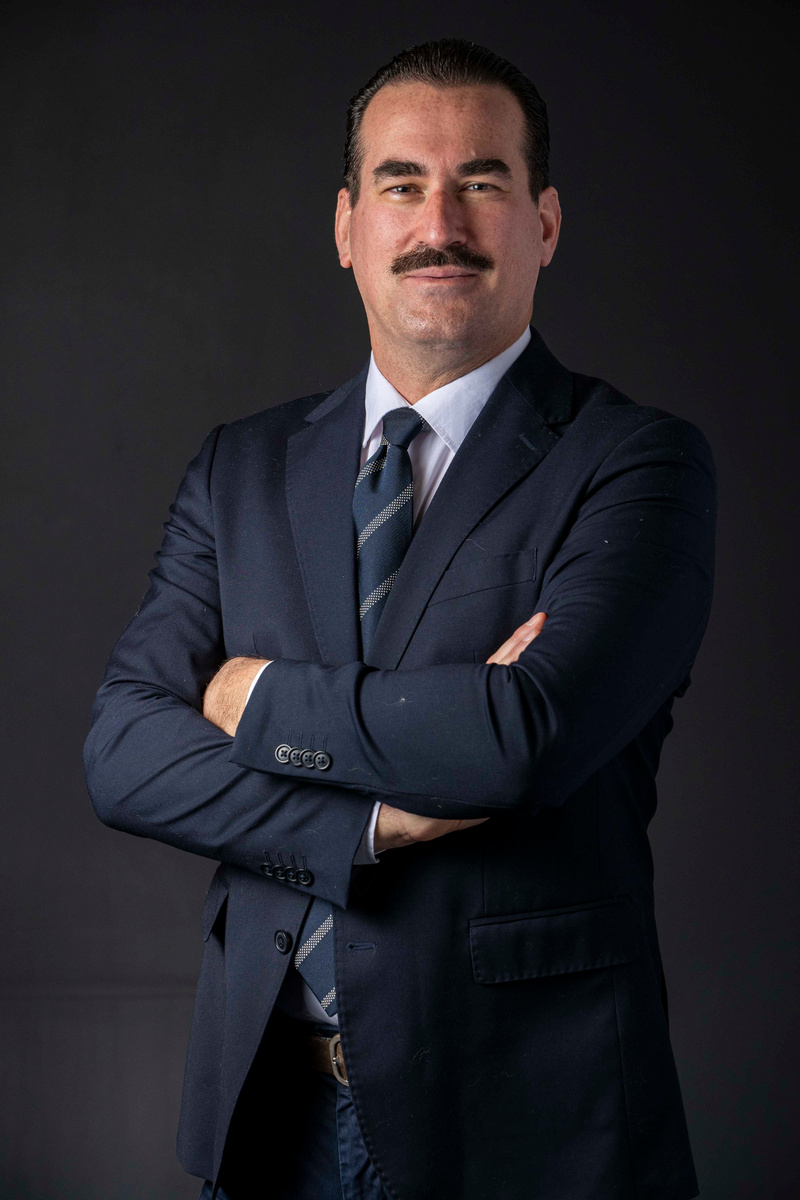
I’m Andrea Mavilla. Over time I have combined technical experience, digital investigation and contextual analysis to turn scattered data into assessments that are useful, readable and responsible.
ANDREA MAVILLACyber Threat Intelligence / Web Reputation
IDENTITY SCAN / VISUAL TRACE
AM / IDENTITY FILEANALYSIS + EXPERIENCE + CONTEXT
AM // BACKGROUND DOSSIER PROFILE / TIMELINE / 08
Experience24+
Years of experience built since 2002 across IT and information security.
ApproachOSINT
Open sources, verification, correlation and careful conclusions.
DomainsCTI
Threat Intelligence, information exposure, Web Reputation and digital identity protection.
MethodEVIDENCE
Every assessment starts from evidence and expands only when context gives it meaning.
01 / PROFESSIONAL BACKGROUND
A path shaped in real-world operations.
From hands-on technical work to intelligence analysis, the underlying thread has remained the same: understand systems and read risk before it becomes a problem.
TIMELINE / 2002 → TODAY
2002 — 2010
The foundations: technical support and operations
My path in information technology began in 2002. During these years I built a practical understanding of systems, technical support and day-to-day technology operations, including work in structured environments such as Valtur.
2010 — 2022
Senior consulting and a wider perspective
The next stage led me into senior IT consulting, with strong experience in Apple environments, device management, cloud services and the operational needs of professionals and organizations.
Today
Threat Intelligence, OSINT and Web Reputation
Today I apply my technical background to digital threat analysis, data correlation and information exposure assessment. This also connects with Web Reputation, digital identity protection and right-to-erasure work, where technology, documentation and human sensitivity must coexist.
IDENTITY / PROFILE MAP
Who I am, in one view.
Not just a professional profile, but a way of reading the digital environment.
CYBER THREAT INTELLIGENCE
RoleThreat Intelligence Specialist
I analyze threats, information exposure and emerging digital risk signals.
ApproachOSINT & correlation
I rely on open sources, data comparison and contextual verification before drawing conclusions.
CapabilityWeb Reputation
I also work on right to erasure, delisting, content updates and digital image protection.
PerspectiveRisk + responsibility
Every piece of information can have an impact. The point is not only to find it, but to understand its real weight.
“I am interested in the point where technology, information and reputation start influencing one another. That is where real digital risk appears.”
02 / METHOD LAB
How I work.
My work is not limited to collecting information. The real value lies in selecting it, organizing it, verifying it and presenting it in a form that helps people understand and decide.
01Observation
I identify relevant information and signals without forcing premature interpretations.
02Correlation
I connect data, sources, dates and context to understand where risk actually emerges.
03Verification
I test reliability, source limitations, potential error and alternative explanations.
04Communication
I turn analysis into clear, documented output proportional to the real impact.
My work moves across different domains, but with one consistent logic: protecting people, organizations and information from both superficial interpretations and real underestimated risks.
CyberThreat Intelligence
I study threats, exposed surfaces, risk patterns and their operational implications.
InvestigationOSINT
Open-source research, monitoring, source verification and complex contextual reconstruction.
ProtectionWeb Reputation
I analyze articles, search results, timelines and protection routes such as delisting and right to erasure.
CommunicationMedia interaction
Many of my investigations have been covered by national and international outlets and entered the public conversation.
04 / PERSPECTIVE
Why I do this work.
I believe a good analysis must first be responsible: able to distinguish an interesting data point from a concrete risk, accessible information from a confirmed compromise, and harmful content from content that simply needs context.
05 / NEXT STEP
If you want to understand a risk, start from context.
Whether it is an OSINT investigation, an information exposure assessment or an online reputation issue, the first step is always to read the situation properly.